A Guide to Chain of Custody for IT Assets
A laptop leaving an employee’s desk is not simply surplus equipment. It may contain customer records, credentials, financial data, intellectual property and licensed software. A clear guide to chain of custody for IT assets turns that risk into a controlled process, from collection through data erasure, refurbishment, redeployment or resale.
For UK organisations, the chain of custody is the evidence trail that shows who controlled an asset, when it changed hands, where it was held and what happened to it. It protects the organisation, its users and the value held in its retired device fleet. If the record has gaps, a signed data-erasure certificate alone may not answer the questions raised by a lost device or a compliance review.
What chain of custody means for IT assets
Chain of custody is a continuous, auditable record of possession and activity. For IT hardware, it begins before collection. The organisation should know which assets are leaving service, their assigned users, their identifiers and their expected destination.
The record then follows the device through every transfer: internal collection, secure storage, transport, intake at a processing site, data sanitisation, diagnostics, refurbishment, resale, redeployment or recycling. Each stage should have a named person or organisation responsible for it.
This is different from a simple asset register. An asset register says that a Dell Latitude laptop exists and belongs to the business. A chain-of-custody record proves that serial number ABC123 was collected from a specific location at a known time, received by an authorised handler and processed according to an agreed method.
The level of detail depends on risk. A small batch of Chromebook devices used for classroom work does not need the same controls as devices used by finance, HR, legal or healthcare teams. But every device carrying a drive, flash storage or removable media needs an accountable route out of service.
Start with an asset release list
The strongest process starts before devices move. Create an asset release list that reconciles the equipment approved for collection against the asset register. Include manufacturer, model, serial number, asset tag, device type, storage type, location, assigned user where appropriate, and any known condition issue.
Serial number capture matters. Asset tags can be missing, duplicated or replaced during a device’s life. A serial number is usually the more durable identifier, while a photograph of the device label can resolve disputes quickly. For Apple Mac hardware, record the serial number and confirm whether Activation Lock or mobile device management controls remain active. For Windows devices, note whether Autopilot registration needs to be removed before resale or reuse.
The release list should also identify exceptions. A device may be missing, damaged, retained for investigation, or still assigned to a remote worker. Exceptions must not disappear from the project because they are inconvenient. Give each one an owner and a follow-up date.
Control collection and handover
Collection is where many otherwise sound ITAD processes become weak. Devices are often gathered in ad hoc piles, carried between offices or sent by untracked courier without a complete count. That creates uncertainty before a refurbishment partner has even received the equipment.
Use a collection manifest for every handover. It should record the collection date and time, collection point, container or seal numbers where used, asset count, identifiers, sender, receiver and signatures or authenticated digital approval. If equipment is collected across multiple sites, create a separate manifest for each location.
For remote workers, provide clear return instructions and tamper-evident packaging where risk justifies it. A tracked service is useful, but tracking alone is not chain of custody. The return must still be matched to the expected serial number and recorded when received.
Secure storage matters during short delays. Retired devices should be held in a controlled area with restricted access, not left in an open office or shared loading space. Record who can access the area, and reconcile the stored count against the collection manifest. This control is simple, but it prevents a common problem: equipment that cannot be accounted for between collection and transport.
Record receipt, condition and data status
At intake, each device should be scanned or manually checked against the manifest. A receipt record confirms what arrived, when it arrived and whether the quantity and identifiers match. Any mismatch should be raised immediately, while records and personnel are available.
Initial condition reporting has two jobs. It supports valuation and identifies potential security or safety issues. Record obvious damage, missing drives, swollen batteries, screen faults, broken ports and signs of unauthorised alteration. Photographs are useful for bulk collections, especially where device condition affects resale value.
Do not assume that a device has been wiped because the previous user signed out, reset Windows or removed files. Those actions do not reliably sanitise every storage area. Mark the data status as unverified until an approved sanitisation process has completed and a result has been recorded.
Make data erasure a controlled event
Data erasure is one of the most important custody points, but it should not be treated as a single tick box. The organisation needs evidence of the method used, the outcome, the device identifier and any failure or exception.
A suitable process may use verified software sanitisation, cryptographic erasure or physical destruction of the storage media. The right method depends on the storage type, encryption state, the device’s intended next use and internal policy. A working SSD in a business laptop may be securely erased and retained for refurbishment. A failed drive may require physical destruction because software verification is not possible.
For each completed device, retain an erasure record linked to the serial number. It should state the sanitisation standard or method, date, processing operator or system, verification result and certificate reference. If a drive cannot be erased, record its removal and the custody route for that component separately.
This distinction protects resale value. Removing every drive by default may feel safer, but it can reduce the usable value of otherwise capable hardware and generate avoidable waste. Retaining a drive without verified erasure is not an acceptable trade-off. The decision must be based on evidence, not assumption.
Separate refurbishment decisions from security decisions
Once data handling is complete, technical assessment can determine the next best use. Devices suitable for reuse may receive diagnostics, component replacement, battery health checks, operating-system installation, cosmetic grading and quality assurance. Equipment that cannot support a reliable second life should be directed to an appropriate downstream route.
Keep these records connected but distinct. A device can pass data erasure and still fail refurbishment because of a damaged mainboard, poor battery condition or unavailable parts. Equally, a visually clean laptop is not ready for resale until its storage has been cleared and its management locks removed.
For resale or redeployment, update the asset status to show its final route. For example: redeployed internally, sold for reuse, parts recovery, storage media destroyed, or sent for material recovery. Record the date of final transfer and the recipient organisation where relevant. This closes the chain rather than leaving the device marked only as “collected”.
Build accountability into the process
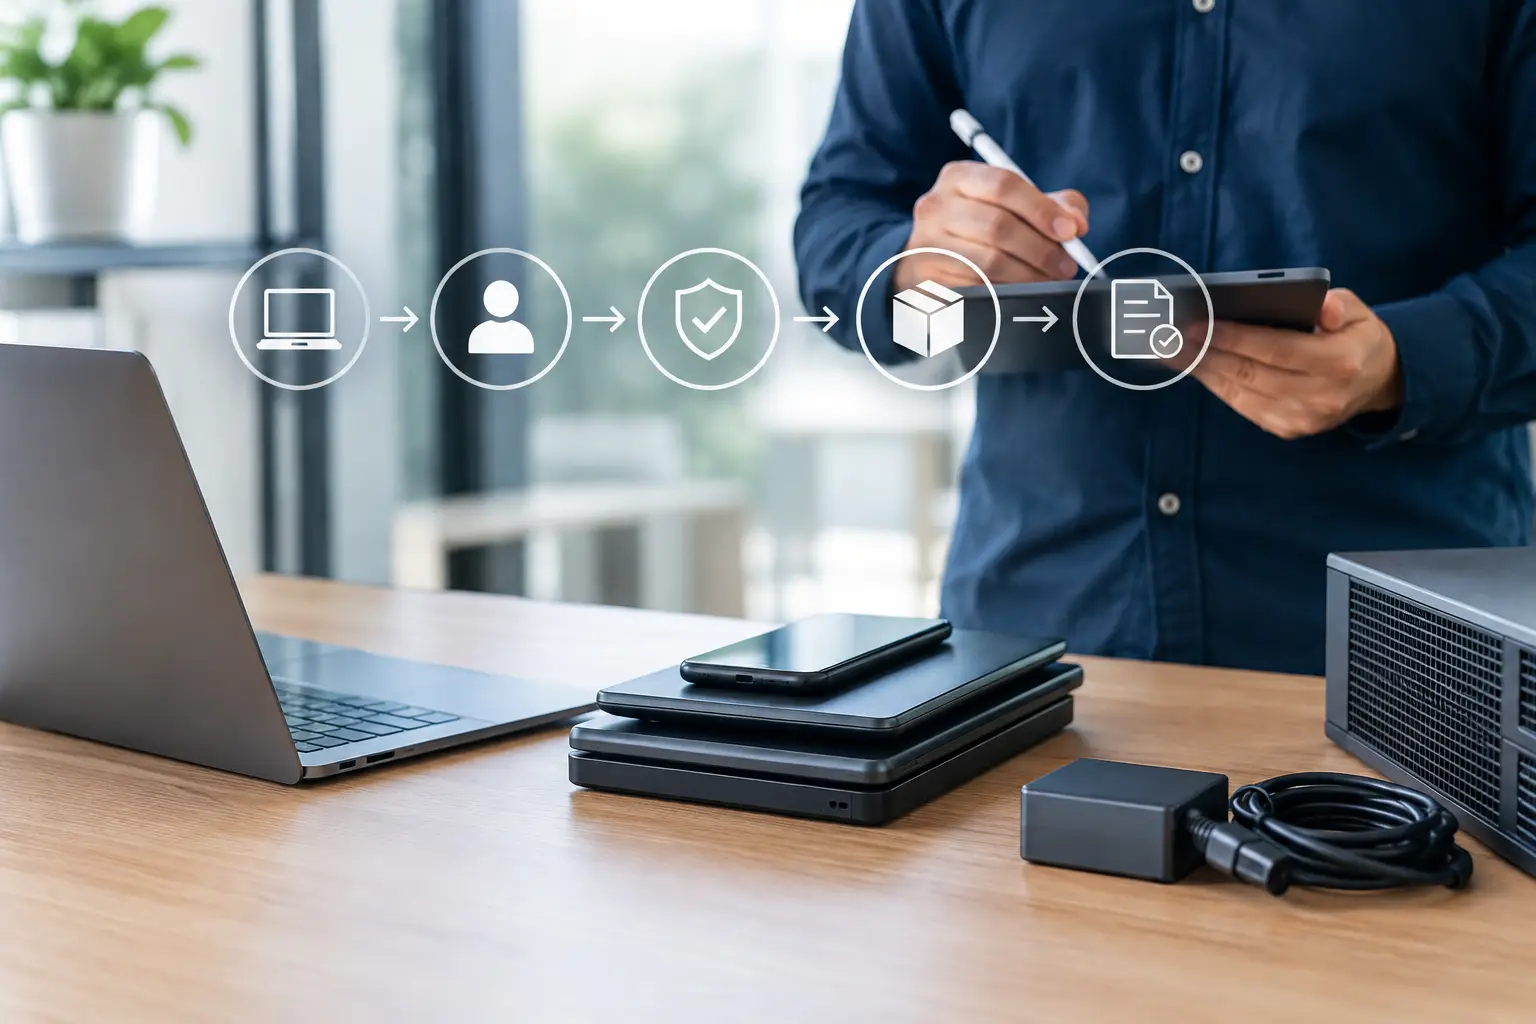
A practical chain of custody does not require excessive paperwork. It requires a small number of records that reconcile with one another: the asset release list, collection manifest, intake record, data-erasure evidence, refurbishment outcome and final disposition record.
Assign clear ownership at each point. The IT team usually owns the source asset data. Site contacts control release. The transport provider controls transit. The ITAD or refurbishment partner controls intake, sanitisation and onward processing. One internal person should remain accountable for reviewing exceptions and confirming that the batch is fully closed.
Audit the process by sampling completed batches. Select serial numbers and trace them from the original register to their final outcome. Check dates, handovers and certificates for gaps. Also review devices that were not received or could not be erased. A chain of custody is only credible when its exceptions are visible.
Refurb X Connect approaches this as a lifecycle record, not a collection exercise. The objective is clear: protect data, retain the value that remains in usable enterprise hardware and provide a defensible record for every outcome.
A well-run custody process makes IT refreshes less disruptive. More importantly, it gives organisations a factual answer when they need to know where a device went, who handled it and whether its data was dealt with properly.