Data Erasure for Retired Business Devices
A retired laptop can still hold years of business activity: customer records, saved passwords, staff files, browser sessions, finance exports and device management data. Data erasure is the control that removes that risk before a device is refurbished, redeployed, resold or recycled. It is not a cosmetic reset. It is a defined process with evidence, checks and a clear chain of custody.
For organisations replacing device fleets, this matters at the point where IT asset management meets data protection. The device may no longer be useful to its original user, but the information on its storage can remain recoverable unless it is handled correctly.
Why deleting files is not data erasure
Moving files to the Recycle Bin does not remove them from a drive. Emptying the bin does not guarantee removal either. In many cases, the operating system simply marks the storage space as available for future use. Until that space is overwritten or the storage is otherwise sanitised, specialist tools may be able to recover the original information.
The same issue applies to a basic operating system reset. A Windows reset, macOS reinstallation or Chromebook Powerwash may prepare a device for a new user, but the right method depends on the device, its storage type, its encryption status and the required assurance level. A reset can be appropriate for a controlled internal redeployment. It should not automatically be treated as verified sanitisation for devices leaving organisational control.
This distinction is particularly relevant for business laptops. A device can look clean at the login screen while still containing recoverable data in unallocated space, recovery partitions, local profiles or attached storage.
Storage type changes the erasure method
Hard disk drives and solid-state drives do not behave in the same way. A conventional hard disk drive stores data magnetically on physical platters. Controlled overwriting can be effective because the process writes new data across the addressable sectors.
Solid-state drives need a different approach. SSDs use flash storage and manage data internally through wear levelling, over-provisioning and garbage collection. These features improve performance and lifespan, but they mean a simple overwrite may not reach every physical location where data has existed. The drive can redirect writes without making that movement visible to the operating system.
For SSDs and modern NVMe drives, a manufacturer-supported sanitisation command or a cryptographic erase method is often more appropriate. Cryptographic erase is effective where the drive has been encrypted correctly from the outset: destroying the encryption key makes the remaining encrypted information unreadable. It depends on the encryption implementation and verification process, so it should be selected deliberately rather than assumed.
Removable media needs separate attention. USB drives, SD cards and external disks are easy to overlook during a refresh project. They are also easy to lose. A complete asset process identifies them, records them and applies an appropriate erase or destruction route.
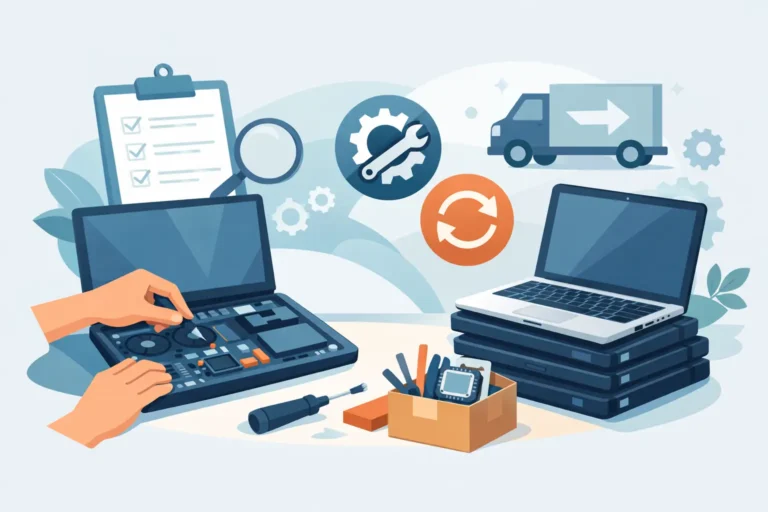
Data erasure is a process, not one command
A reliable workflow begins before any erasure software runs. Each asset needs to be identified, logged and tracked from collection through to its final outcome. That record should include the device type, manufacturer, model, serial number or asset tag, storage configuration and intended destination.
The device is then assessed. Technicians need to know whether it contains a hard drive, SATA SSD, NVMe SSD, soldered storage or multiple drives. A laptop may have an internal drive plus a second drive, or a removable module that needs separate handling. Faulty devices need care too. If a drive cannot be accessed or sanitised through a verified process, physical destruction may be the appropriate route.
After erasure, verification matters. The process should confirm that the chosen method completed successfully and that the storage is no longer accessible through normal recovery routes. A failure should not be treated as a pass because the device appears to start normally or because its previous user account has gone.
Finally, the result should be documented. A certificate or erasure report creates an audit trail showing what was processed, when it was processed, which method was used and whether it passed. For a fleet of several hundred devices, this evidence turns a potentially opaque disposal exercise into a manageable control.
What good evidence looks like
A useful erasure record is specific enough to support internal governance, customer assurance and an audit. It should tie the outcome to the individual asset, not just state that a batch of devices was handled.
At a minimum, retain the device identifier, storage serial number where available, erasure software or process used, date and time, pass or fail status, and the operator or processing location. If a device has multiple drives, the record should show each one. A certificate that only references a laptop serial number can leave a gap if the drive has been changed during its life.
The required level of reporting depends on the organisation. A school managing a small Chromebook refresh may need a clear device list and confirmation of completion. A business handling sensitive client information may require fuller reporting, staged approvals and documented collection controls. Public sector and regulated environments may have additional requirements set by their own policies and contracts.
Erasure, refurbishment and resale
Secure erasure is one of the steps that makes refurbishment viable. Once a device has been cleared, its hardware can be inspected, tested and graded without carrying the previous owner’s information into the next stage of its lifecycle.
That is good for security and for value recovery. A business-grade Dell, HP or Lenovo laptop may still have years of practical use after its first deployment. With tested storage, a clean Windows installation, battery assessment and quality checks, it can support a new employee, student or home user at a lower cost than a new equivalent device.
The same principle applies to Apple Mac devices, tablets and desktop systems, although each platform has its own account and management controls. Activation Lock, Find My, mobile device management enrolment and firmware settings must be removed through authorised processes before resale. Data erasure alone does not resolve an ownership lock.
For Chromebooks, administrators should also remove the device from the organisation’s Google Admin console when it is no longer part of the managed fleet. Otherwise, a wiped device may still enrol back into the former organisation’s management environment when it connects to the internet.
Common gaps in device retirement
The biggest failures are rarely technical edge cases. They are operational gaps: devices held in drawers, unrecorded home-worker equipment, drives removed from laptops, equipment passed directly to staff, or collections arranged without a verified inventory.
A better approach is to set a repeatable retirement policy. Define when devices are collected, who approves disposal or resale, how assets are recorded, what erasure method applies to each storage type, and what happens when an erasure attempt fails. Make the process usable for remote workers as well as central offices.
It is also sensible to separate data decisions from resale decisions. A device should be cleared to the required standard before anyone assesses its resale value. That keeps commercial recovery from influencing the security outcome.
Choosing a refurbishment partner
When devices leave your organisation, ask practical questions. Can the provider identify and report each device? Do they distinguish between HDDs, SSDs and NVMe storage? What happens to failed drives? Can they provide individual erasure evidence? How are account locks, management enrolment and non-working equipment handled?
The answers should be straightforward. A provider should be able to explain the route from collection to testing, erasure, refurbishment, resale or responsible recycling without vague assurances. Refurb X Connect treats secure processing as part of the device lifecycle, not an add-on after the hardware has already changed hands.
Data protection and sustainable IT can support the same outcome. When data is removed properly, usable devices can stay in circulation rather than becoming avoidable e-waste. The next device refresh is a good moment to make that process measurable: know what you hold, know what leaves, and retain evidence that its data has gone.